

Application security testing tools help in identifying and fixing vulnerabilities across app code, runtime environments, APIs, and dependencies. The leading app security testing tools 2026 combine SCA, DASD, SASD, and mobile application security testing to ensure top-notch security of the app throughout the development life cycle. This comprehensive guide covers some of the top application security testing tools that are a boon for modern DevSecOps teams.
Why Application Security Testing Can’t Wait Until Release
Current-day applications face ever-rising security risks as teams strive to fix them. Integrating the best application security testing tools into development workflows themselves helps in identifying and addressing problems before they can go into production.
Test on real devices. Ship with confidence.
- With rising vulnerability exploitation resulting in a whopping 31% of breaches, surpassing stolen credentials is becoming increasingly common (Source: Verizon 2026 DBIR)
- The same source indicates that only 26% of critical vulnerabilities were attended to in the previous year, calling for more stringent measures for the time to come
Also Check Out: Rooted Android devices for mobile security testing
The Four Types of Application Security Testing
Application security testing takes different approaches to identifying vulnerabilities at varying stages of the software development life cycle. While SCA, IAST, DAST, and SAST take into account code application risks, if we add an additional layer to validate security controls on mobile environments and real devices, there has to be mobile-specific security testing.
SAST (Static Application Security Testing)
- What it does:
It conducts an analysis of app source code without executing it to recognize security weaknesses in the earlier stages of development.
- When it runs:
It runs on every code commit during development.
- Findings:
Insecure data flows, buffer overflows, hard-coded credentials, and SQL injection patterns
DAST (Dynamic Application Security Testing)
- What it does:
It sends malicious payloads and simulates attacks against any exposed interfaces.
- When it runs:
DAST runs against pre-production or staging environments pre-release
- Findings:
Cross-site scripting, runtime configurations, API vulnerabilities, authentication, bypass issues, etc.
IAST (Interactive Application Security Testing)
- What it does:
IASD monitors app behavior during runtime through application instrumentation during test execution
- When it runs:
It runs during automated test execution and functional testing.
- Findings:
I runtime data flow problems and business logic flaws with reduced false positives in comparison with using dast or SAST alone.
SCA (Software Composition Analysis)
- What it does:
SCA performs a scan of open-source components as well as third-party libraries to recognize known compliance problems and security risks.
- When it runs:
It runs continuously during dependency updates and builds.
- Findings:
Common vulnerabilities and exposures independencies, as BOM requirements, and license compliance violations.
Mobile-Specific Security Testing
- What it does:
Mobile-specific security testing is a crucial Mobile App Testing pillar that validates mobile app security controls by conducting testing on real mobile environments and hardware.
- When it runs:
It runs continuously throughout the entire application life cycle as well as during pre-release validation
- Findings:
SSL traffic interception vulnerabilities, behavior problems, risks associated with biometric authentication bypass, certificate pinning issues, jailbreak and root detection gaps.
Also Read: Types of Mobile App Testing
Top 10 Application Security Testing Tools in 2026
Application security testing tools help businesses detect as well as remediate vulnerabilities across applications, source code, APIs, dependencies, and mobile environments. The appropriate AppSec tools 2026 stack combines SCA, DAST, and SAST along with mobile security testing to enhance security overall.
Category 1: SAST Tools
1. SonarQube
SonarQube refers to a leading open-source static analysis platform that helps developers in identifying bugs, security vulnerabilities, and code quality issues in the early stages in the development lifecycle.
- What it is: It is an open-source SAST platform responsible for scanning source code for various vulnerabilities as well as quality issues across more than 30 languages.
- AI layer: Offers AI-powered suggestions for fixing issues and integrates with AI coding assistants to provide real-time IDE feedback.
- License: Community Edition is available as an open source solution, with commercial tiers also available to organizations.
- Best for: Testing and development teams that require continuous code security scanning and are also integrated with IDEs as well as CI/CD pipelines.
- Key limitation: Results with SAST results often contain false positives and need context-based validation.
2. Checkmarx One
Checkmarx One refers to an enterprise app security platform, which is a combination of multiple security testing capabilities all stacked together into a unified workflow.
- What it is: It’s a cloud-native platform that offers SAST, IaC scanning, API security, SCA, and container security along with AI-assisted remediation.
- Best for: Big enterprise teams that require unified AppSec coverage along with developer-focused remediation workflows.
- Key limitation: Enterprise pricing with that level of complexity might be unsuitable for smaller teams.
3. Veracode
Veracode offers a wide-ranging application security platform suitable for organizations that require remediation guidance, vulnerability detection, and compliance support.
- What it is: AppSec platform that covers SAST, DAST, SCA, and penetration testing with developer-friendly remediation insights.
- Best for: Enterprises that require comprehensive security testing along with compliance reporting.
- Compliance angle: Offers reporting capabilities most commonly utilized in regulated industry security programs.
Category 2: DAST Tools
4. OWASP ZAP (Zed Attack Proxy)
OWASP ZAP refers to a famous open-source DAST tool to identify vulnerabilities in web applsand APIs.
- What it is: It’s an open-source DAST scanner, OWASP-maintained for automated as well as manual security testing.
- License: Apache 2.0.
- CI/CD integration: Supports GitHub Actions, Docker, and REST API integrations.
- Best for: Security teams and DevSecOps engineers who need free web and API vulnerability scanning.
- Key limitation: Advanced configurations might need additional security expertise.
Test on real devices. Ship with confidence.
5. Burp Suite
Burp Suite is a popular web security testing platform appropriate for manual penetration testing with vulnerability assessment.
- What it is: It’s a proxy-based security testing tool featuring automated scanning along with manual testing capabilities.
- Best for: Security engineers as well as penetration testers assessing web apps and APIs.
- Key limitation: Most advanced features are available only in paid editions.
6. Invicti
Invicti is a widely used enterprise DAST platform that focuses on automated vulnerability discovery and enhanced accuracy.
- What it is: It’s a leading DAST solution that uses proof-based scanning for confirming vulnerabilities and reducing false positives.
- Best for: Enterprise teams that need highly scalable automated security testing.
- Key advantage: Assists security teams so that they’re able to prioritize confirmed vulnerabilities.
Category 3: SCA Tools
7. Snyk
Snyk is popular a developer-focused security platform that assists teams secure open-source dependencies all through development workflows.
- What it is: It’s an SCA platform scanning dependencies for CVEs, offering fix recommendations, and generating SBOMs.
- Best for: Development teams who wish to integrate dependency security directly into IDEs as well as CI/CD pipelines.
- BFSI angle: SBOM capabilities offer support for software supply chain transparency needs.
8. Black Duck (Synopsys)
Black Duck facilitates management of compliance requirements, open-source security risks, and software supply chains at the enterprise level.
- What it is: It’s an enterprise SCA platform for license compliance, vulnerability detection, and SBOM generation.
- Best for: Big organizations with strict compliance needs and complex dependencies .
- Key limitation: Appropriate mostly only for enterprise-scale environments.
Category 4: Mobile Application Security Testing
9. Appknox
Appknox has its primary focus on mobile app security testing for organizationsthat are building iOS /Android applications.
- What it is: A popular mobile security platform that offers automated DAST, SAST, and API security scanning with compliance reporting.
- Best for: Mobile teams that need automated security checks during release cycles.
- Key limitation: Cloud-based testing might require additional data handling considerations.
10. Pcloudy (Real Device Mobile Security Testing)
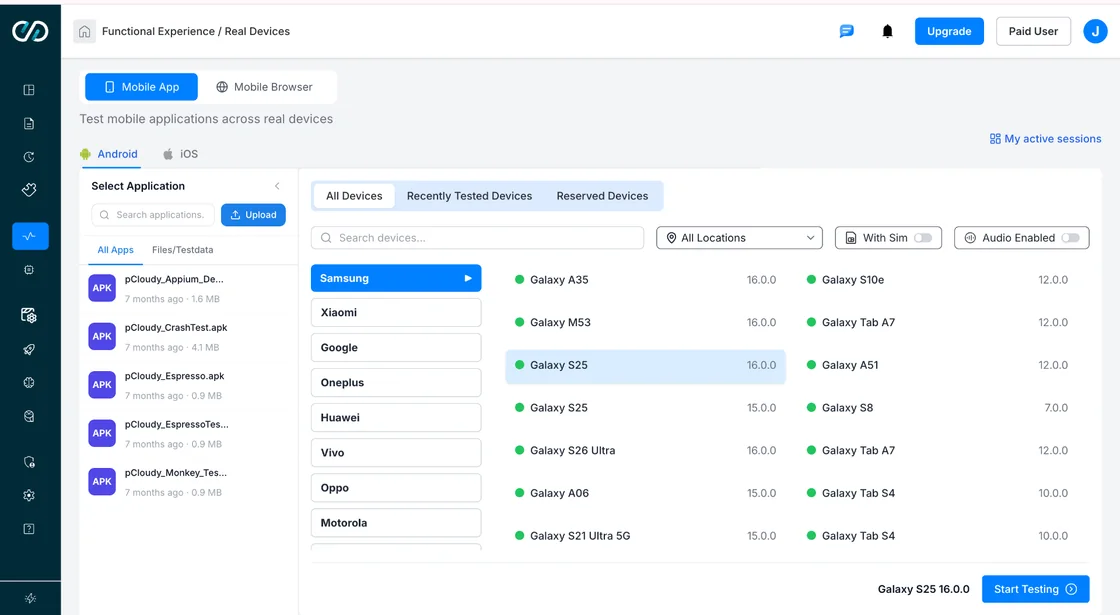
Pcloudy enables top-notch mobile security testing on 5000+ real devices with the aim of validating security controls traditional AppSec tools and most emulators aren’t able to completely replicate.
- What it is: Highly trusted real device cloud with single-tenant hardware, Frida support, rooted Android devices, and compliance-ready testing environments.
- What it validates: Pcloudy validates root detection, Play Integrity behavior, jailbreak detection, biometric bypass, certificate pinning, and Frida-based attack scenarios.
- Why real devices are needed: Real device hardware enables security testing scenarios at an OS-level that standard emulators as well as shared cloud devices aren’t able to fully support.
- Compliance: Supports ISO 27001, SOC 2 Type II, and PCI-DSS compliant testing requirements along with audit-ready testing records.
- Best for: FinTech, Banking, and mobile teams that could use secure real-device validation for vital mobile apps.
Direct Comparison: Application Security Testing Tools
| Tool | Primary Security Testing | Best For | Key Highlights |
|---|---|---|---|
| SonarQube | SAST | Secure code analysis | Open source, offers support for 30+ languages, IDE as well as CI/CD integration |
| Checkmarx One | SCA, SAST, IaC | Enterprise app security | Unified platform containing AI-assisted remediation |
| Veracode | DAST, SAST, SCA | Enterprise + regulated industries | Compliance reporting with governance features |
| OWASP ZAP | DAST | Web + API security testing | CI/CD-native, open-source, automated vulnerability scanning |
| Burp Suite | Manual Penetration Testing, DAST | Security engineers and penetration testers | Industry-standard toolkit for both manual and automated testing |
| Invicti | DAST | Enterprise web application security | Proof-based scanning featuring a reduced false positive rate |
| Snyk | SCA | Developer-first dependency security | In-IDE fix recommendations with SBOM generation |
| Black Duck | SCA | Software supply chain security | License compliance and enterprise open-source governance |
| Appknox | Mobile SAST, DAST | Mobile app security | Android and iOS scanning with compliance reporting |
| Pcloudy Real Device | Real Device Mobile Security Testing | Mobile security validation | Rooted real devices, BFSI-ready, SOC 2 and ISO 27001 compliance |
How to Choose the Right Application Security Testing Tools
Opting for the right application security testing tools relies on the type of applications, your organization’s security goals, and compliance requirements. Here’s how businesses can choose the appropriate application security testing tools for their unique needs.
- Compliance requirements: Opt for tools that offer audit-ready evidence for standards such as FFIEC, PCI-DSS 4.0, and MAS TRM.
- Code security: Leverage the power of SAST tools such as Checkmarx One, SonarQube, or Veracode for detecting vulnerabilities during development.
- Dependency security: Use SCA tools such as Snyk and Black Duck to recognize risks in open-source components.
- Runtime security: Utilize DAST tools such as Burp Suite, OWASP ZAP, or Invicti to test running applications as well as APIs.
- DevSecOps adoption: Combine DAST, SCA, SAST, and mobile security testing to ensure continuous protection across the SDLC.
- Mobile security: Use mobile-focused tools like Appknox and Pcloudy to validate mobile security controls on real devices.
Why Banking and FinTech Applications Need Additional Testing Coverage
Fintech and banking applications need stronger security validation due to the immense impact vulnerabilities can have on regulatory compliance, customer data, and financial transactions. Let’s check out why they need deeper cross code coverage, audit requirements, and mobile security.
Continue Security Across Software Life Cycle
Financial applications require continuous SCA, DAST, and SAST testing well integrated into development pipelines that includes remediation, tracking, security evidence, and regular scans to help teams maintain a certain level of protection throughout each release.
Real Device Mobile Security Validation
Mobile banking apps require testing for security controls such as SSL interception, certificate pinning, root and jailbreak detection, and biometric authentication. Real devices need accurate validation of such scenarios.
Compliance-Driven Security Testing
BFSI applications need security testing evidence that aligns with standards like MAS TRM, FFIEC, and PCI-DSS 4.0. Security testing tools should be able to generate vulnerability records, compliance documentation, and audit-ready reports.
Also Check Out: Mobile Banking Application Testing, The Ultimate Guide to Performance Testing for Banking Applications
Conclusion
Choosing the appropriate application security testing tools helps QA teams secure applications across the entire SDLC and adhere to compliance requirements. A robust AppSec strategy exhibits a combination of SCA, DASD, SAST, and mobile security testing to provide a layer of protection against evolving threats to modern applications. If you want to take your mobile app security testing on real devices to the next level, start your 30-day Pcloudy free trial today and validate security controls on real devices with the utmost confidence!
FAQs
What is application security testing?
Application security testing is responsible for identifying and fixing vulnerabilities in application code, APIs, dependencies, and runtime environments.
What is the difference between SAST and DAST?
While SAST checks source code for any security issues, DAST tests running apps for real-world vulnerabilities.
Why do mobile apps require separate security testing tools?
Mobile apps require testing for device-specific controls such as root detection, biometrics, and certificate pinning.
Can you use emulators for mobile application security testing?
Emulators may help with basic testing but aren’t able to fully validate real device security behavior, unlike real device testing.
What security testing is required for banking and FinTech apps?
BFSI applications need mobile security testing, SAST, SCA, DAST, and compliance evidence for staying compliant with standards such as PCI-DSS 4.0 and FFIEC.


 Jeroline


